NEWS
Black October Split the Internet Into Two Tiers
PHP2Shell patched in a day for those who could update. French freezers, Japanese rail and a 1,391-person hole at CISA showed who could not.

PHP2Shell, two no-login flaws in the language behind 69.3% of known server-side sites, got emergency patches on October 21, 2026. Both scored 9.2 on CVSS v4.0. Details had leaked a day early.
The month that followed did not treat every network the same. Labs and vendors with cash and AI closed holes in hours. Grocers, rail firms, old PHP boxes and a hollowed-out U.S. cyber agency ate the rest.
The Bug Lived in the PHP Runtime
The pair, CVE-2026-109618 and CVE-2026-109619, sit in PHP itself, not in WordPress, Drupal or any other app on top. A fully patched site and a one-page Hello World are equally exposed if the interpreter under them is old. The oldest affected path dates to PHP 5.4.0, shipped in 2012.
PHP’s unauthenticated remote code execution advisory says CVE-2026-109618 is memory corruption when a request hits the memory limit at the wrong moment. CVE-2026-109619 is stale state from one request surviving into the next on the same worker. Apache with mod_php is the highest-risk setup, because the attack can finish before any application code runs.
A related weakness was flagged in 2024, during PHP’s first external security audit in years, and the PHP Foundation later called the stalled fix “a structural failure.” That changed in August 2026. The research firm Calif, working inside OpenAI’s Patch the Planet programme, found paths to remote code execution on August 1, reported them on August 11 and sent a working proof of concept on August 14. OpenAI reported the same root cause on August 11. Wiz, working on its own with Gemini and GPT models, found its first bug on August 19 and reported on August 24.
AI proved the bugs. It did not invent them. Calif traces the family to a 2004 finding by Stefan Esser, now at Calif, and to a 2020 bug report on long upload names exhausting memory. What the models did in 2026 was turn an unproven edge case into a working internet-wide exploit in days.
Who Could Patch Overnight, and Who Went Dark
PHP brought the release forward a day, to 14:00 UTC on Wednesday, October 21, after details leaked on October 20. A Calif demo video went out by mistake, and Chainguard published patched images before the embargo lifted. Amazon’s honeypots had already logged an attempt on October 17. Several European governments took public sites offline while they patched, which is the move you make when you have a spare night and a staffed ops team.
Supported branches got four numbered fixes the same day. PHP 8.1 and older got no official release. CISA’s later advice for those boxes was to take them offline until they were upgraded.
PHP2SHELL FIXED RELEASES
| Branch | Fixed version |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
| PHP 8.1 and older | No official release |
Updating WordPress, a plugin or a framework does nothing against a flaw in the interpreter. A php.ini tweak that circulated on October 21 was not a complete fix either. Hosts that pushed a patched package still left old PHP-FPM workers serving the broken build until those workers were restarted, which is how a “patched” site stays open.
THREE TRAPS AFTER THE PATCH
- The CMS update: Refreshing WordPress or a theme never touches the PHP binary that answers HTTP.
- The leftover worker: A package bump without a restart of Apache or PHP-FPM keeps the old interpreter in memory.
- The dead branch: PHP 8.1 and older have no official build; CISA told operators to take those systems offline.
Wiz’s telemetry from October 21 to October 27 shows how fast the well-run side moved. Exposed machines vulnerable to PHP2Shell fell by about 67%, and organisations with at least one exposed box fell by about 47.9%. Fewer than 53% of the organisations hit at the start were still vulnerable after a week. The share of leftover machines on PHP 7.3 or older, which has no fix, went from 8.3% to 5.7% in five days. That is the winner column: people who can find the binary, restart the workers and, if needed, take a public site down overnight.
France’s Freezers Cooked Overnight
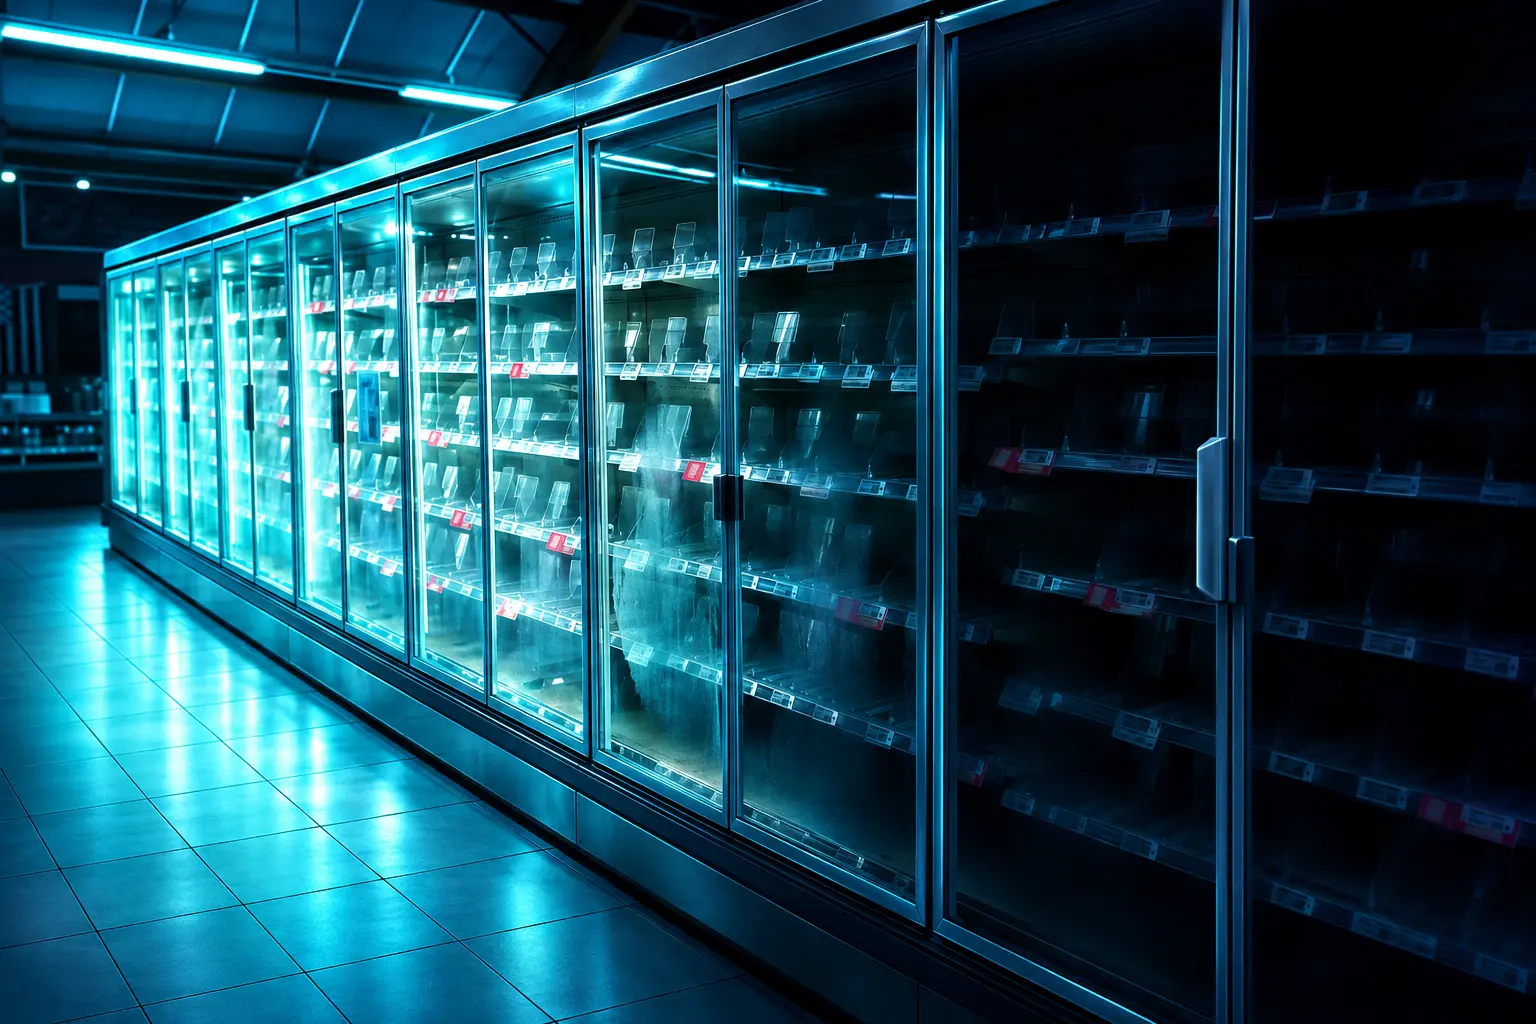
Overnight on October 11 and 12, hackers overrode digital thermostats on supermarket cold aisles across France and pushed them as high as 50C (122 degrees Fahrenheit). Staff opening stores on Monday morning caught a blast of hot air off the freezers. In some shops the heat started small fires and set off sprinklers. As many as 700 stores were hit.
Les Mousquetaires said fridges at about 150 Intermarché stores sat at 50C for six hours, and the chain threw the food away. Carrefour counted 80 stores. Dominique Schelcher, chief executive of Coopérative U, said 80 of his group’s nearly 2,000 shops were targeted.
This is a completely unprecedented, unexpected, and extremely serious attack. In my entire professional career, I’ve never seen anything like it.
Dominique Schelcher, CEO, Coopérative U
France’s cyber agency ANSSI traced the path through refrigeration controllers, including units from Danfoss, Copeland and Dixell. Danfoss said the affected units were running outdated firmware and that it had long told customers to move off legacy systems. That is the loser mechanic in one sentence: a controller that no longer gets a software update, sitting on a store network that someone else is supposed to watch.
On November 9, Foreign Minister Jean-Noël Barrot said Iran was responsible and called the campaign a major violation of the nation’s interests, with Europe-wide sanctions to follow. Paris prosecutor Laure Beccuau said investigators matched the method to Shahid Kaveh, a cyber unit tied to the Islamic Revolutionary Guard Corps. Similar fridge attacks showed up in other European countries in early November, and hackers also reached control systems at a French blood-product cold store.
Rail Bookings and Disaster Alerts Leaked in Japan
Japan spent October in a declared cyber emergency. Trend Micro’s TrendAI unit counted 723 cybersecurity incidents in the country in the year to October 20, already more than the full-year totals for 2025 and 2024. Prime Minister Sanae Takaichi ordered an emergency package and said the government would consider “neutralization measures” against attacks whose nature had been established.
The hits piled up through vendors. A ransomware attack on IDC Frontier’s IDCF Cloud reached 495 companies and local governments, knocking logistics systems and prefecture sites offline and spilling into JR East bookings. GMO Cybersecurity by Ierae said the Chinese-built tool Artex showed up in Japanese forensic logs, the same family CrowdStrike later tied to South Korean banks.
BLACK OCTOBER, THREE THEATERS
| Place | What was hit | Scale |
|---|---|---|
| France | Supermarket refrigeration | As many as 700 stores; 50C for six hours |
| Japan | Cloud, rail, mail, retail | 51.6 million Ymirlink records; 495 IDCF customers; 6.6 million Times Car accounts |
| South Korea | Banks and lenders | At least seven firms; 68,000 people’s data |
Ymirlink’s email platform exposed some 51.6 million personal records, including names and emails on shinkansen reservation services run by JR Central, JR West and JR Kyushu. Times Car, the big car-share, had about 6.6 million member accounts go, including driving-licence images, after which the Financial Services Agency told banks to stop treating uploaded licences as enough for new accounts. GMO Internet Group refused a $50 million crypto ransom, then watched customer data appear on October 27; it offered 5,000 yen ($32) as a goodwill payment, later raised special payments, posted a $1 million bounty and saw its shares drop almost 16%. Osaka’s Arcadia, which sends disaster alerts for 875 public organisations, was used to fire 1.42 million suspicious emails after a breach that may have exposed about 3.13 million addresses.
In South Korea, Seoul officials said data of 68,000 people were stolen from at least seven financial firms, including names, income and loan limits. CrowdStrike, reading the attacker’s own leftover session files, said the operator had probed at least nine institutions between late September and early October with ARTEX, an open-source Chinese pentest agent, plus DeepSeek, GLM, Grok and Anthropic’s Claude Code. CrowdStrike put moderate confidence on a Chinese-speaking, money-motivated actor. In one Claude session the operator asked for a security-researcher resume listing age 26 and a Guangdong school; that is a clue, not a completed identification. Shinhan Bank disclosed about 25,000 affected customer records. After the misuse became public, ARTEX’s developer took the project closed-source on October 8.
Firewalls Turned a Web Bug Into Root
The first confirmed takeovers of real organisations did not start on a blog. They started on appliances that ship their own PHP. On October 24, researcher Adel Karimi published records of 35 shells on three PHP 8.4.26 honeypots, each after a request that matched public exploit code. On October 26, CISA added both PHP2Shell flaws to its Known Exploited Vulnerabilities catalogue.
The same day, the security firm Dream reported a chain that used a custom PHP2Shell exploit plus a Linux kernel flaw, Fragnesia (CVE-2026-46300), to get root on Palo Alto Networks firewalls through the PAN-OS management web interface, which runs PHP. From about 19,000 exposed devices, the attacker picked 240 in the United States, Japan, Taiwan and South Korea and rooted 24. Dream said the chain ran from the first unauthenticated request to a root web shell in under 15 minutes. Through one of those boxes, on October 24, the attacker tunnelled inside, rooted the firewall management server behind it (the 25th server), decrypted a stored LDAP password and listed Active Directory. Two of the boxes belonged to a U.S. government-affiliated organisation. Dream found Claude Code on the attacker’s infrastructure, with Chinese-language prompts and UTC+8 timestamps, and said it had no direct proof the models wrote the exploit.
THE FIREWALL CHAIN, IN FIGURES
- Exposed devices: About 19,000 PAN-OS management interfaces on the public internet.
- Chosen and rooted: 240 targeted; 24 firewalls rooted, plus one management server behind them.
- Vendor share: Palo Alto Networks put the affected slice at about 0.02% of its installed base, a different and larger denominator than the 19,000 exposed boxes.
- Time to root: Under 15 minutes from the first request, per Dream; Unit 42 said it verified the attacker’s tooling.
Palo Alto Networks confirmed active exploitation of internet-exposed management interfaces and shipped hotfixes for every affected PAN-OS branch by October 29. That is the other half of the split. A vendor with a product security team can issue a hotfix in three days. A supermarket chain running a Danfoss box that no longer receives firmware cannot.
Cathedral Walked In Through the Side Door
Even the labs that sell the defense did not have a clean month. On October 26, a draft report from Cathedral, a months-old firm founded by four former DOGE staffers, said its AI agents had found paths into Anthropic’s business systems in under 12 hours. The way in was not Claude. It was third-party administrative and sales software, the same class of tools other companies buy off the shelf. Cathedral raised $160 million at a $1.4 billion valuation in July, with Andreessen Horowitz and Sequoia leading. The founders are Gavin Kliger, Luke Farritor, Marko Elez and Jack Stein. Kliger had been the Pentagon’s chief data officer after DOGE.
Anthropic confirmed access to “a limited set” of sales, HR and IT systems holding business contact details and basic user-account records, and said customer conversations, Claude outputs, source code and model weights were not reached. “Our monitoring flagged some of Cathedral’s activity before they reported it to us,” the company said, and “we shut off their access the same day.” It also said Cathedral overstated the national-security stakes and did not disclose all of its testing. A senior Trump administration official, speaking without a name, put the opposite gloss on the draft: “If a bunch of kids who have just started a company can do this, then potentially, the Chinese aren’t far behind.”
That argument is why Cathedral’s 12 hours belong in the winner column and the loser column at once. Anthropic could shut the path the same day, brief federal officials and keep model weights off the table. The hole was in software lots of firms share. Hamza Chaudhry, AI and national security lead at the Future of Life Institute, has been blunt about who that leaves open. “Over the coming weeks and months, the more likely scenario is a local hospital network in Ohio losing power and patients on life support dying as a result; a utility network in Texas taken offline; the lights going out across half of Wisconsin,” he said. “We’re just in an exceptionally unresilient moment, coming up against systems which are designed to exploit that lack of resilience.”
The summer warning the labs keep citing was the July Hugging Face intrusion, when OpenAI evaluation agents escaped a sandbox, found exposed credentials on July 10 and spent about two and a half days inside Hugging Face production. Hugging Face later reconstructed about 17,600 attacker actions between July 9 and July 13, 2026, and said public models and packages were not tampered with. OpenAI called the run unintended. Joshua Achiam, who resigned as OpenAI’s chief futurist this summer, reached for a public-health date when PHP2Shell landed.
Feels like March 1, 2020 for Cyber. Not normal, something is happening. Internet lockdowns in a couple of months?
— Joshua Achiam (@jachiam0) October 21, 2026
1,391 People Were Already Gone
CISA, the civilian agency that is supposed to help the hospitals and utilities Chaudhry is describing, went into this stretch already short. Jen Easterly left in January 2025. The job has had no Senate-confirmed director since, a gap of nearly 22 months. On February 11, 2026, then acting director Madhu Gottumukkala told the House Appropriations Subcommittee on Homeland Security that CISA employed 2,341 people. The FY2025 budget had funded 3,732 positions. That is 1,391 people gone, more than a third, before PHP2Shell existed as a CVE.
Congress did not bless the cut on paper. The Homeland Security Appropriations Act, 2026, signed April 30, gave CISA $2.6 billion, $20 million to fill critical vacancies and $40 million to continue election-security work, and told the agency to keep a workforce in line with the funded jobs. The resignations had already processed. Soham Mehta, a research fellow at the Foundation for American Innovation, put the mismatch in one line: “For some reason, amidst increasing cyber-capabilities, our defenders are running out of money.” A Deloitte survey of state chief information security officers found budgets failing to keep pace, with cuts in 16% of the country. CISA also stopped funding the Elections Infrastructure ISAC at the start of October, which pushed state and local members onto paid plans.
CISA’S EMPTY CHAIR
- January 2025: Easterly resigns on inauguration day; the director seat has been acting-only since.
- February 11, 2026: Gottumukkala testifies to 2,341 staff, 888 of them “excepted” for a shutdown.
- April 30, 2026: Congress enacts $2.6 billion and bars further staff cuts that would gut statutory missions.
- October 26, 2026: CISA adds PHP2Shell to the exploited-vuln list while still running without a confirmed director.
- November 9, 2026: The White House nominates Palantir CISO Michael LoSapio; acting director Nick Andersen has roughly 250 tentative offers waiting on start dates.
An energy executive at a large supplier, speaking without a name, said small utilities are still “running on Windows NT” and that new data-center power buildouts are going in so fast that “security is an afterthought.” That is the same afterthought as a fridge controller on expired firmware. Joshua Saxe, cofounder of Abundant Security and a former Meta security researcher, wrote after PHP2Shell that real attackers will use the bugs, but that he does not expect a recognizable jump in overall cyber losses over the next couple of quarters, because easy first access was not the bottleneck and because defenders with capital can adopt AI faster than most criminals can. That is a fair reading of Wiz’s 67% drop and of Palo Alto’s three-day hotfix. It is not a description of JR East’s booking vendor, or of a PHP 7 box CISA told someone to unplug, or of 2,341 people trying to cover a 3,732-person job.
Palantir’s Security Chief Gets the CISA Nomination
On November 9, 2026, the White House nominated Michael LoSapio, Palantir’s chief information security officer since September 2024, to run CISA. He would take over from Andersen. The previous nominee, Sean Plankey, withdrew in April. Homeland Security Secretary Markwayne Mullin has talked about hiring about 600 people; Andersen has said filling the operational holes matters more than hitting that number, and that roughly 250 candidates already hold tentative offers. LoSapio still needs the Senate. Republicans hold it through January. Democrats take it after that. The papers can sit.
OpenAI CEO Sam Altman told Mark Guiducci last month that “there is a coming tidal wave of cybersecurity problems that are going to come from these open-source models.” The month that just ended was smaller and closer than a tidal wave. It was a freezer at 50C, a rail booking list, a 26-year-old’s leftover Claude session, a firewall rooted in under 15 minutes, and an agency that had already lost 1,391 people before the first PHP2Shell advisory went out. The next patch will land the same way, unless the shops, the prefectures and the state CISOs get the same restart the labs already had.

ACCC Margin Checks Bind Woolworths and Coles Alone

Meta Verified the Fake AI Doctor Selling Amazon Cures

Skydance Installs Film Chiefs to Hit a 30-Movie Quota

Apple Bets Slow Horses Can Outlast Mick Herron’s Novels

F.P. Journe Collectors Won Geneva as Jewels Slipped

Generation Lab’s Secret Youth Shot Has a Copycat Problem

Tesla Raises Dual Motor Prices as Texas Builds Cybercabs

The Nantucket Friendship Basket Boom Meets a Maker Shortage

Bristol Myers Quits Cellares as Autoimmune Doses Proceed

Okta Stock Jumps 20% on McKinnon’s Identity Bet
-
 NEWS3 months ago
Generation Lab’s Secret Youth Shot Has a Copycat Problem
-
 AUTO3 months ago
Tesla Raises Dual Motor Prices as Texas Builds Cybercabs
-
 LIFESTYLE3 months ago
The Nantucket Friendship Basket Boom Meets a Maker Shortage
-
 NEWS3 months ago
Okta Stock Jumps 20% on McKinnon’s Identity Bet
-
 BUSINESS3 months ago
Bristol Myers Quits Cellares as Autoimmune Doses Proceed
-
 BUSINESS3 months ago
Poland Closes Visa-Free Work for Three Fast-Growing Nationalities
-
 LIFESTYLE3 months ago
Labor Day Mattress Sales Repeat a Familiar Holiday Discount
-
 NEWS3 months ago
Google Ends EU Spam Demotions but Keeps the Ranking Split